The enforcement phase arrived. In the first quarter of 2026 alone, California regulators issued more than $4 million in fines over opt-out implementation failures — Disney at $2.75M, PlayOn Sports at $1.1M, Ford at $375K. Read the pattern rather than the dollar figures: these are not cases about missing privacy policies. They are cases about mechanisms that existed on the page and did not work end to end.
That makes this an engineering problem, and the specific failures are ones a developer can test for.
The baseline obligation, as of January 2026
Twelve states now require businesses to honor universal opt-out mechanisms: California, Colorado, Connecticut, Delaware, Maryland, Minnesota, Montana, Nebraska, New Hampshire, New Jersey, Oregon and Texas. In practice that means Global Privacy Control — a browser or extension signal, not a click on your banner.
Two implementation facts follow.
GPC arrives as a header and a DOM property, and you have to check both. The Sec-GPC: 1 request header reaches your server; navigator.globalPrivacyControl === true is what client-side code can read. A consent platform configured to read only one of them will miss traffic. Your server-rendered pages and your edge cache rules see the header; your tag manager sees the property.
A signal is not a banner interaction. GPC must be honored without the user touching your consent UI, and it must not be overridden by a subsequent “accept all” that the user never meaningfully chose. Several enforcement actions have turned on exactly this ordering bug: the signal was read, then a default or a banner state wrote over it.
California added a further requirement effective January 1, 2026 — a business must visibly confirm to the consumer that an opt-out request has been received and processed. That is a UI change with a state dependency behind it, not a toast message. If your front end says “done” before the downstream propagation has been enqueued, you have built the thing regulators have been fining.
Deletion has a platform now, and a clock
California’s Delete Act platform, DROP, went live January 1, 2026, and registered data brokers were required to begin processing requests through it from August 1, 2026. Broker registration carries its own January 31 deadline and penalty structure.
Most teams reading this are not registered data brokers, but the downstream effect is real: if you sell or share data with one, their deletion obligations propagate to what you sent them, and the reconciliation questions land on whoever owns the pipeline.
For general requests — deletion, opt-out of “sale” — most state laws still allow 45 days. Forty-five days is comfortable for a synchronous database delete and tight for anything involving a warehouse, an archive tier, a search index, backups, and three SaaS destinations that each have their own API and their own idea of what “deleted” means.
What to actually verify in your own stack
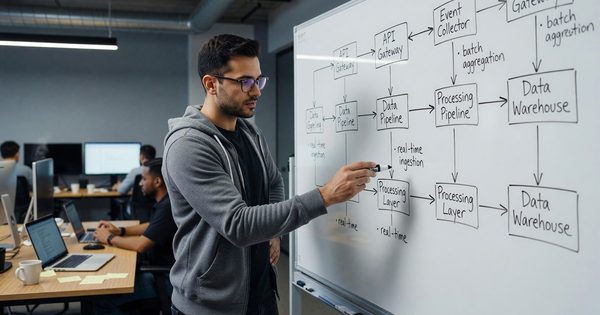
Trace one opt-out end to end, with logging at every hop. Signal received → consent state written → tag manager consent mode updated → server-side event collection suppressed → destination platforms informed. The fine-generating failures are almost always at hop four or five, where a server-side pipeline keeps sending because it never learned about a client-side decision.
Test with the signal, not with the banner. Install a GPC-sending extension or set the header directly and load the site cold. Then check: does any tracking request fire before the consent state resolves? Race conditions between an async consent platform and a synchronously-loaded tag are the single most common technical defect here.
Check your edge. Cached HTML served from a CDN can carry a consent state baked in from another visitor. If consent affects what is in the response body, the Sec-GPC header needs to be part of the cache key — or that content needs to come out of the cached document entirely.
Enumerate where a person’s data physically exists. Write the list down: primary database, read replicas, warehouse, event archive in object storage, search index, CRM, email platform, support tool, analytics vendor, backups. Then, for each, answer “what does a deletion request do here, and how long does it take?” The entries where the answer is “nothing, currently” are your gap list, and the 45-day clock does not care that one of them is a vendor’s problem.
Confirm the confirmation. Given the January 2026 requirement, the user-facing acknowledgement must reflect that the request was actually recorded. Tie it to the persisted state, not to the click handler.
Build it as a service, not as a page
The teams that handle the growing state patchwork without rewriting their consent logic every January have one thing in common: opt-out state is a first-class record, addressable by user and by pseudonymous identifier, readable by every producer in the stack, with an audit trail of when it changed and what caused the change. Jurisdiction-specific rules then become policy on top of that record rather than branching logic scattered through the front end.
That design also gives you the thing you will need most when a regulator or a customer asks: the ability to answer, for a specific person on a specific date, what your systems were permitted to do and what they actually did. Twenty states with slightly different rules is a configuration problem if you have that record, and an archaeology project if you do not.